Keyll · API key abuse protection
Keyll the Gemini key. Not the project.
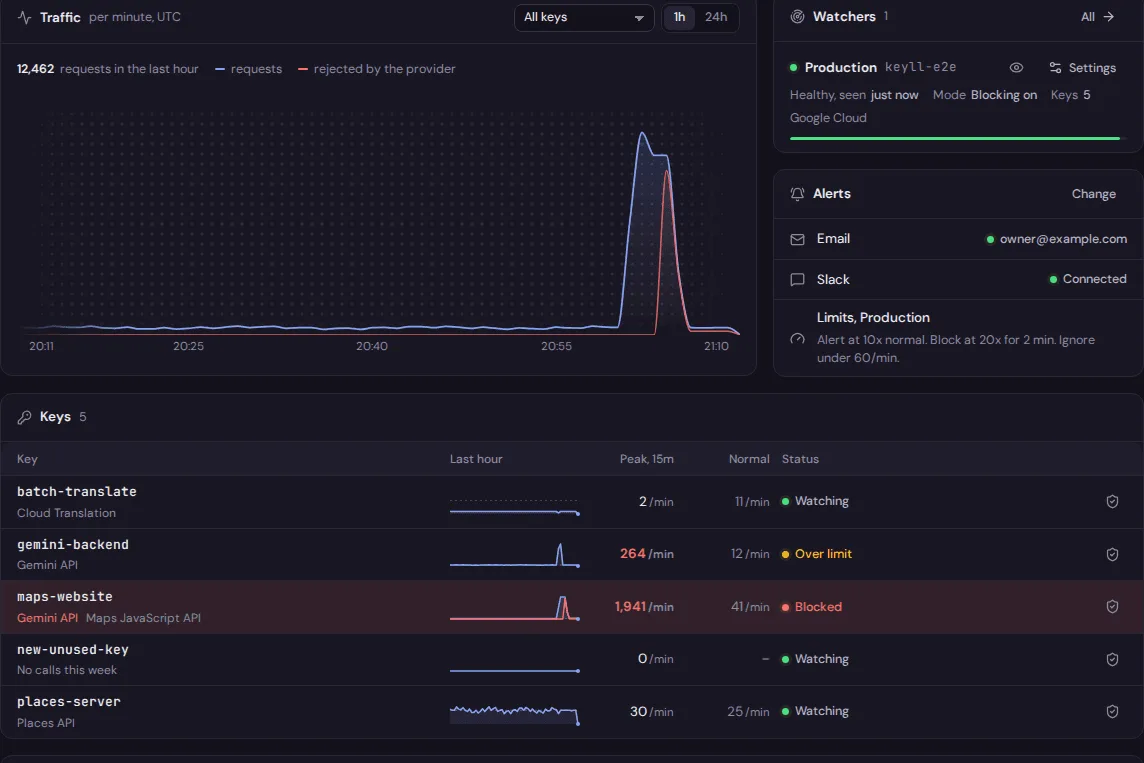
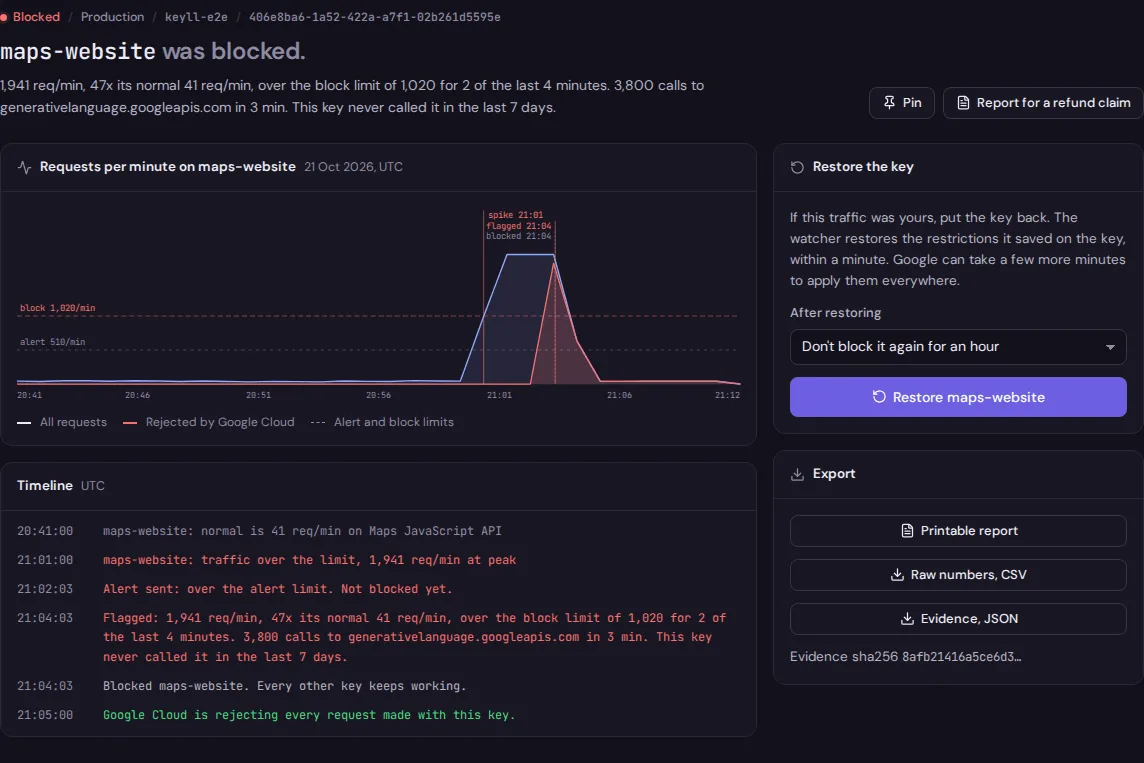
Keyll watches usage on every API key you connect, on Google Cloud, Anthropic, OpenAI, OpenRouter or Resend, and blocks the one being abused. Every other key keeps working.
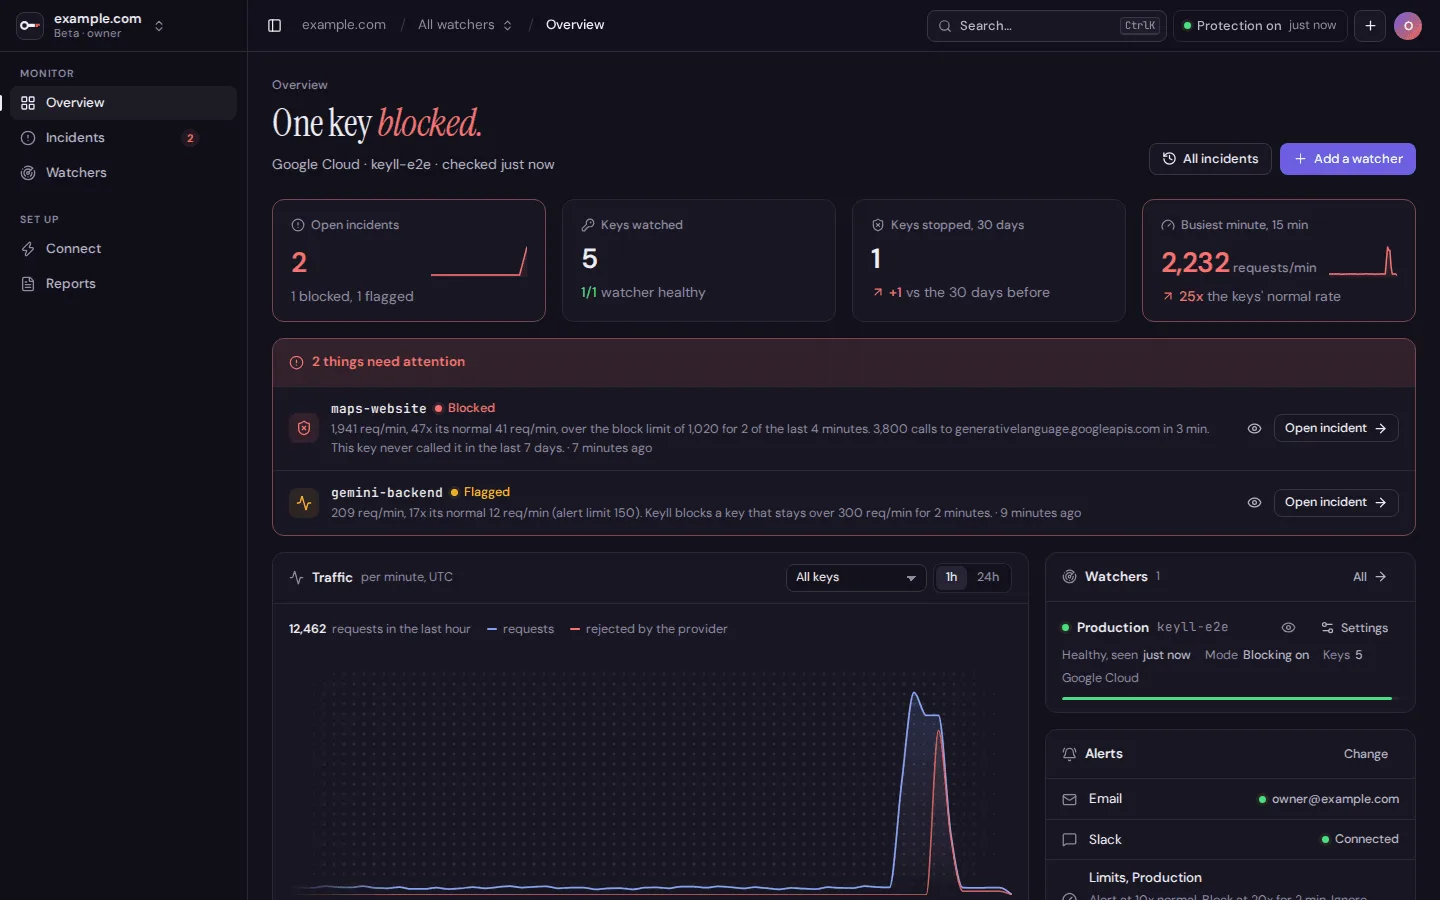
Watches per-key usage on
Gemini API, Anthropic, Maps, OpenAI, Google Cloud, OpenRouter, Cloud Translation, Firebase, Resend.
The cost of a leaked key
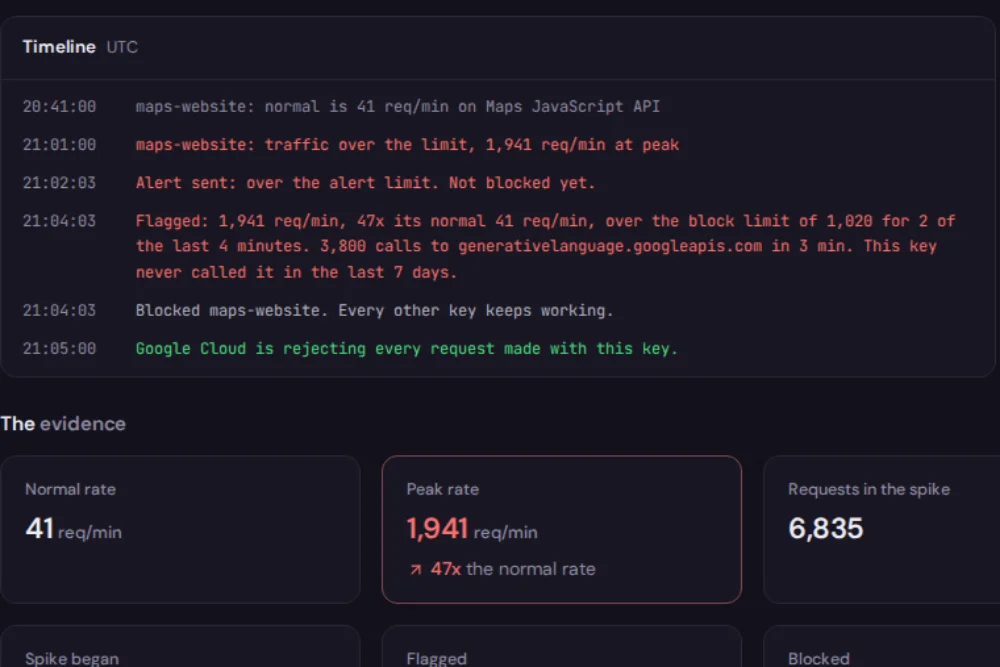
The bill is rate times minutes. Attackers set the rate. Keyll cuts the minutes.
- Time to a block
- ~20 min
- on Google Cloud, with Keyll's defaults
- Monitoring delay + 20 min over the limit
Surprise bills, everywhere
A spending cap didn't stop any of them. Each one links to the original report.
$82,314
Gemini API · Mexico · Feb 2026
A three-person startup's stolen key ran image and text models for two days.
$10,000
Google Cloud · Australia · May 2026
Billed despite a $250 spending cap.
$127,000
Google Cloud · May 2026
The account was locked for non-payment, and so were the logs needed to dispute it.
$30,000+
AWS Bedrock · May 2026
Marketplace charges skip Cost Anomaly Detection, so no alert ever fired.
One bad key shouldn't take down the rest
A small watcher runs in your Google Cloud project or on your own server, and holds the only credentials. Keyll decides, but the watcher only runs a block that Keyll signed and that fits the limits you set on your side. Key strings never leave your environment.
Got questions?
Not yet. The dashboard and the watcher run end to end against an emulator of each provider. Join the waitlist for one email at launch.
On Google Cloud, a custom role with four: read request counts, list and read keys, and update a key's restrictions. It can't read key strings. Anthropic, OpenAI and OpenRouter have no narrower credential, so there the watcher needs an admin or management key. Either way the credential stays where the watcher runs, and Keyll holds none.
It alerts within minutes. On Google Cloud a block lands about 20 minutes in: the provider's reporting delay, 10 minutes of sustained abuse, then a 5-minute warning you can cancel.
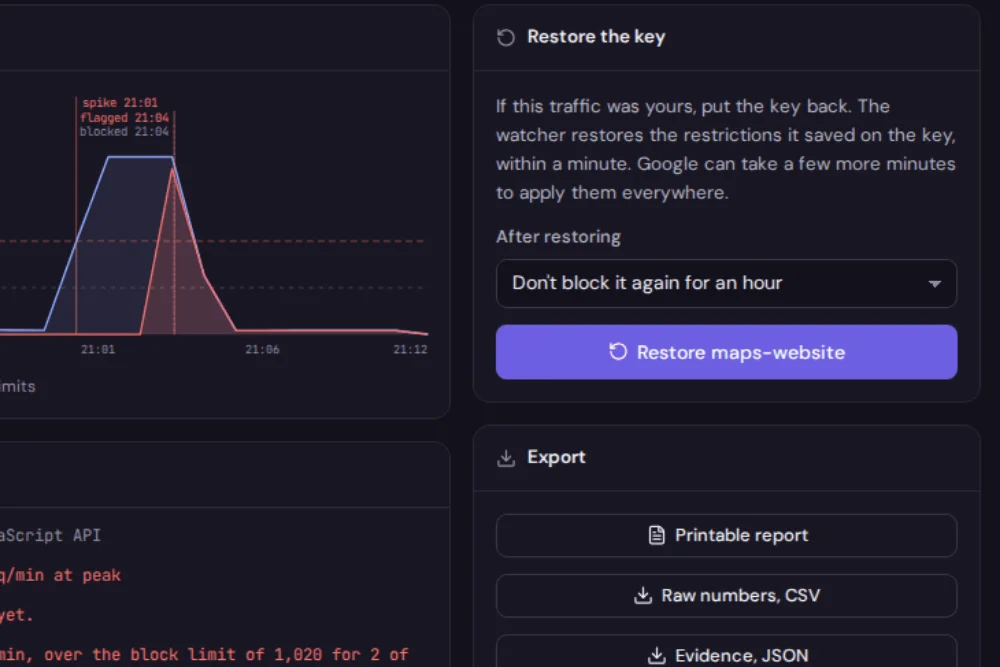
You get a warning before each block and can cancel it. After a block, one click undoes it: a Google Cloud key gets back the exact restrictions saved on it, and Anthropic and OpenRouter keys are switched back on. The watcher starts in dry run and blocks at most 3 keys an hour.
Google Cloud keys (Gemini, Maps, Firebase, Vertex AI and the rest), Anthropic, OpenRouter, OpenAI and Resend. OpenAI and Resend keys get alerts unless you opt in to blocks: OpenAI's API doesn't say what a key's permissions are, and Resend can only delete a key. AWS and Supabase are planned.
$15 a month at launch; the waitlist is free. Dispute help is the incident report, CSV and evidence hash plus the steps for a billing case. The refund is the provider's call; Keyll pays nothing out.
Leaked a key? Start here
Free, step-by-step guides for revoking an abused API key, finding what it cost, and capping the next bill.
Find out in minutes, not on the invoice
Free to join. $15 a month at launch, with dispute help included. One email when Keyll ships, then we delete the list.